Can fighting website hackers help protect the planet?
When we think about the "security" of our websites, any link with "ecology" seems remote, even far-fetched. And yet hacking has a real and significant energy cost. Where does this energy impact come from, and how can we fight it? Here are some answers.
Who are the hackers, and what do they target?
Hackers have changed a great deal over the last decade. Forget the cliché of the teenager hiding in his basement behind his keyboard and glasses, who cracks his school library's password and might put his nickname on the local bakery's website to show off to his hacker friends.
No, real modern hackers are organised, and they do not just go after a handful of specific sites. Hackers target every site. Everyone is a target. Their goal? To attack everywhere to increase their chances of "success", and ultimately make as much money as possible through advertising, spam or phishing. To get there, they have no scruples and, of course, no ethics. Anything goes.
Is my site vulnerable?
As we have seen, everyone is a target, which means that if you have a website, there is roughly a 100% chance that it will be attacked. The real question is therefore whether or not your site is secure.
Generally speaking, sites that are not maintained and have not been properly secured are the most vulnerable. But it is above all CMSs (WordPress, Joomla, Drupal and others) that are targeted, because they are so widely used.
Indeed, a CMS, being popular by nature, will inevitably have security flaws discovered in it over time. "Perfect" code that is completely invulnerable for ever and ever, while also being rich in features, does not exist yet. As soon as any interaction with the user or site visitor is possible, a flaw is potentially possible too.
These "flaws" or "vulnerabilities" are unintentional open doors in your site's PHP code that allow unauthorised access to files, data or features. Exploiting them can range from "being able to send spam" to "gaining full control over the site's files and database".
Once discovered, these flaws are usually made public for two main reasons: either to force the vendor to release a fix, or, once fixed, to show how dangerous they were and encourage users to update. Software vendors generally fix these flaws very quickly, but if a site is not kept up to date, it becomes very easy to hack.
So, since you are certain to be attacked, make sure you are not vulnerable by avoiding the 7 cardinal security mistakes in webmastering.
How hackers operate
The "easy" way for a hacker to take control of as many sites as possible quickly and automatically: develop programs that scan every site looking for known vulnerabilities in the major CMSs.
Some hackers often start by finding unsecured web servers on which to place their hacking scripts and/or bots. With several servers, they build themselves a remotely controlled "war machine". This set of servers is called a "botnet".
They then compile the most complete lists possible of every known website, then lists of known flaws, and program a way of testing for these flaws across a whole set of sites. Their botnet then sends huge numbers of requests to each listed site in search of a flaw that will let them take control of it. If a site is vulnerable, the hacker can then exploit it.
There are of course also brute-force attacks, in which the bot tries every possible password and username. Administrator access to a site also makes it possible to take control of it.
What the hacked site is then used for ranges from defacement to sending spam or mining cryptocurrencies, not to mention redirects to advertising sites or scams, or the creation of phishing pages on the site.
Ultimately, attacks aimed specifically at one particular site are rare: in the vast majority of cases, we see mass attacks that target sites more or less at random, regardless of how popular they are.
A significant energy cost
It is easy to forget, but every request to a website requires a certain amount of processing power from the server's CPU, and that processing power requires electrical power: the server consumes a certain number of watts every time a page is loaded. How much depends on how well the site is optimised.
Now, the hacking attempts described above all have one thing in common: a huge number of pointless requests are sent to the servers hosting the sites. This generates heavy CPU usage and therefore a sharp rise in power consumption.
An idle server uses little energy, thanks in particular to the power-saving features provided by Dell and Intel in the servers we use. But a CPU under full load consumes a considerable amount of electricity, with the extra consumption ranging from 50 to 300 watts per server depending on its capacity.
Beyond the phase of probing for flaws and attempting to hack, using a hacked site can then also require a great deal of energy. The worst case is when the site is used to "mine" cryptocurrencies.
Although it is hard to measure, we estimate that without any preventive action, more than 75% of the requests handled by web servers are probably hacking attempts. A significant share is also used by search engines.
A double energy penalty
Direct power consumption is one thing. But in a datacentre, the rooms are air-conditioned so that the servers can run properly in a dense environment (the servers are "racked" on top of one another). In a datacentre, if you use more energy for computing, you then use more energy for cooling.
Although our own datacentre is cooled in an environmentally responsible way (an evaporative cooling system using rainwater, which requires less electricity), most datacentres use conventional air-conditioning units that are very energy-hungry. The consumption caused by bots is therefore very substantial, especially on a global scale.
Why and how to fight back
We will never be able to stop attacks, but we can defend ourselves and block them, thereby avoiding the needless consumption of resources and energy. From deterrence to elimination, several means of protection exist.
The webmaster: deterrence
On the one hand, the webmaster has a role to play in deterrence. By securing their site, the webmaster can "help" the hacker (or hacking bot) realise quickly that it is wasting its time: the site is up to date, there is no known security flaw, so there is no point carrying on. As long as the attack is even slightly sophisticated, it should die down quickly. Above all, this keeps the site from being hacked.
The webmaster can also install security modules that automatically block attacking IPs, for example the WordFence plugin for WordPress, which (among other things) protects against brute-force attacks.
The webmaster can also use the security tools provided by their host. HaiSoft offers a number of them, which we will look at shortly.
Finally, a secure site is a site that will not be hacked and will therefore consume less electricity.
So there is everything to gain from protecting yourself.
The host: the (strong) armed wing
On the other hand, a host such as HaiSoft naturally has a major role to play in this fight and can prevent many attacks.
At HaiSoft, several automatic security measures are in place. They filter attacks, detect them and block the attackers' IPs. Once an IP is blocked, its requests no longer reach the servers and the problem is avoided.
Obviously, a host must use state-of-the-art software and configure sensitive access with great rigour in order to prevent any intrusion, or even block any intrusion attempt, using port or IP filtering.
We have also found that frequent manual monitoring is needed to counter attacks that slip through the net of the automatic systems. Sometimes the "load" (server usage) generated by a hacking bot is not enough to slow our server down and trigger a monitoring alert. That is why we have also set up real-time monitoring systems that let us check resource usage regularly, effectively and in greater detail.
Here is an example: instead of more or less random usage peaks (typically page loads), usage becomes constant (pages being loaded non-stop by a bot).

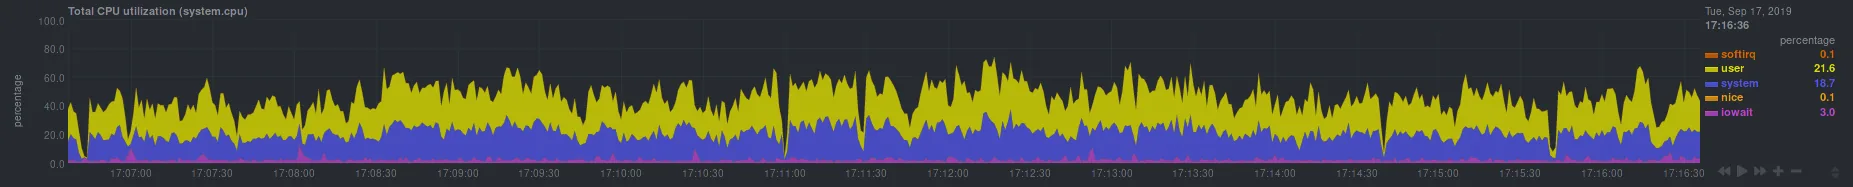
Thanks to graphs like these, we know when there is abnormal activity on a server, and we dig deeper to block the handful of IPs attacking sites on it.
The measures taken by HaiSoft
Here, for example, are the main measures built into HaiSoft shared hosting:
- Anti-brute-force protection (Fail2ban) on many services, including the WordPress login
- A web application firewall blocking dangerous requests, bot scans and hacking attempts (and triggering IP bans by Fail2Ban when they are repeated)
- Port and IP filtering on sensitive services
- WordPress Toolkit, including security features that can trigger Fail2Ban blocking, plus additional anti-bot detection
- Frequent, detailed checks of resource usage to detect attacks, and manual blocking of attacking IPs
Do you have a VM or a dedicated server? We offer to apply all of these measures free of charge for all our VM and dedicated server customers, as part of the managed services included with all our servers.
Results
These measures have cut CPU usage on our shared servers by a factor of three to four, drastically reducing our power consumption. They have also brought server load down to a manageable level, dramatically improving site response times. Combined with the simultaneous move of our servers to SSDs, performance is now better than ever.
The drawback is that certain situations can trigger false positives. For example, if a file that is forbidden from access is called on every page of your site, you trigger an error on the web server with every click: the repetition of these errors can be mistaken for an attack, and your IP gets blocked. This occasionally calls for a new kind of support, but it has greatly reduced the number of requests about slow sites.
Site hacks have become less frequent since these measures were introduced. However, as we have also worked hard to get users onto more recent PHP versions and to update their scripts, it is difficult to know how much of this is down to the security measures.
Conclusion: a fight that everyone wins
The great thing about this fight is that everyone wins:
- Site owners get better security and speed, and are hacked less often
- Hosts reduce their energy consumption and see fewer support requests
- Our planet's resources are saved
Is your site secure? Does your server have the protections described in this article? Feel free to contact HaiSoft for more information.